Spamhaus DROP
High-confidence hostile IPv4 and IPv6 ranges can be blocked at the managed router before traffic reaches services behind it.
IT Communications
Protect your business connection with AI-powered threat analysis, continuous monitoring, automatic response and customer portal visibility.
AI-Powered Network Protection Built Into Your I.T Communications Service
Active, not passive
A conventional internet circuit delivers traffic and leaves you responsible for everything crossing it. Supported I.T Communications managed connections can add continuous visibility, automated threat response and reporting through the same service relationship.
We provide the connection, the managed network and the intelligent protection layer around it.
AI built into the protection layer
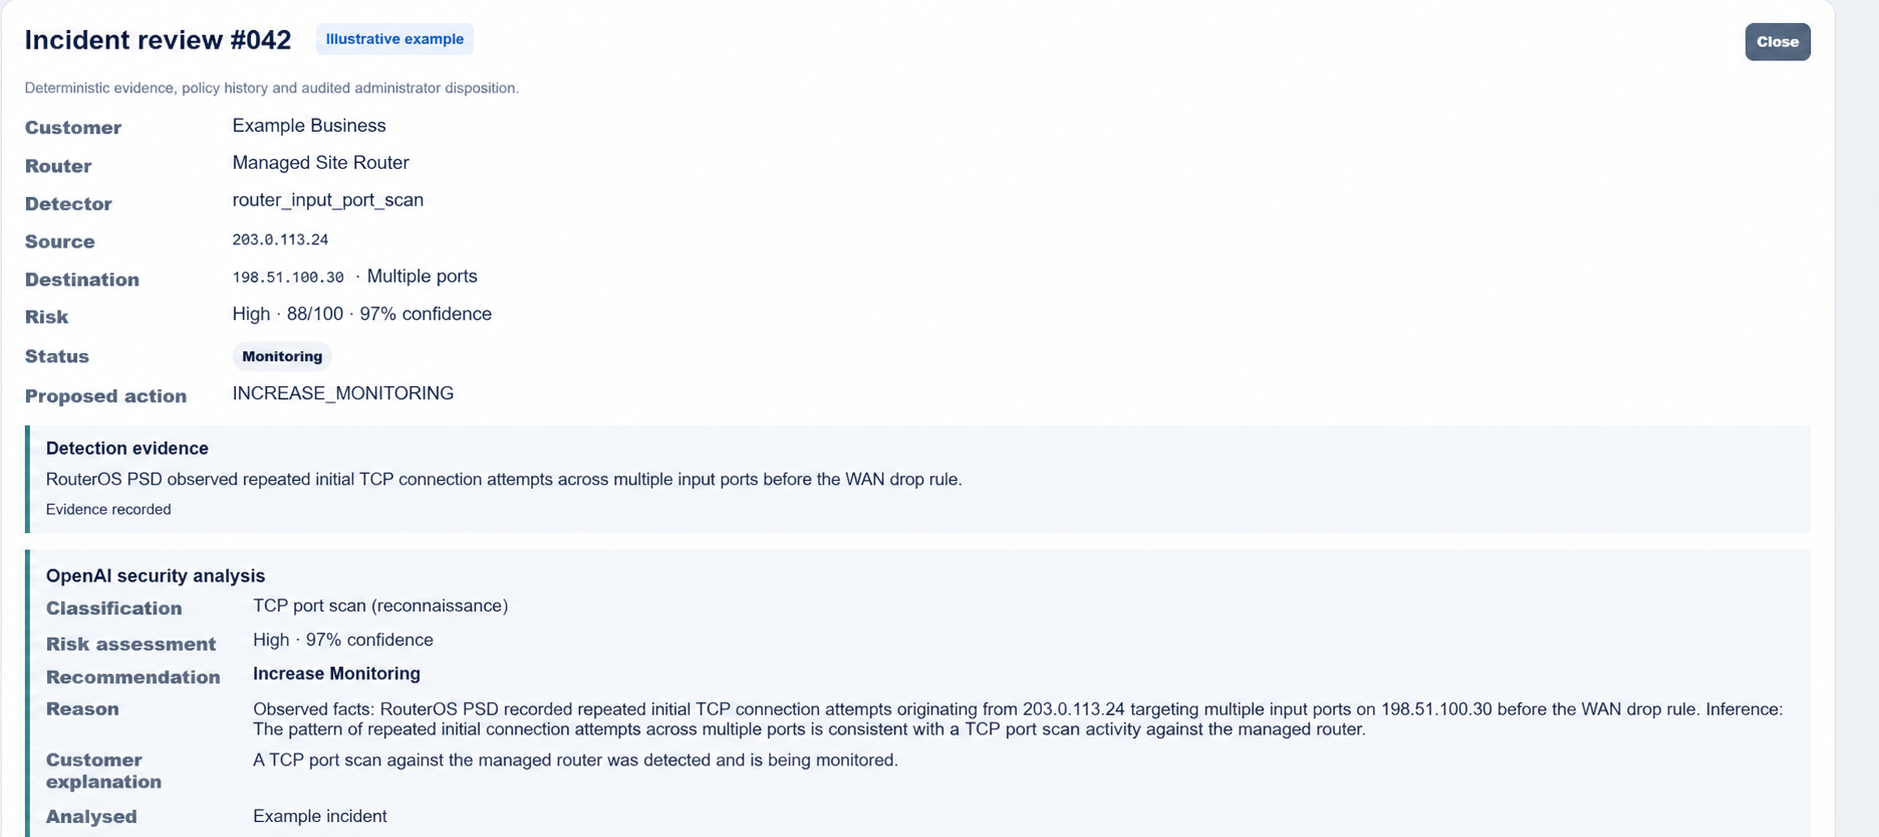
Active Network Protection combines high-speed network detection with built-in AI analysis. AI helps interpret suspicious behaviour, correlate events, assess context and turn technical activity into explanations people can understand.
Protection does not rely solely on AI. High-speed security rules handle immediate threats while AI adds deeper analysis and context, so protection continues if the AI service is temporarily unavailable.
Real-time protection
Designed to identify activity consistent with port scanning, repeated connection attacks, abnormal connection rates, router management attacks, suspicious SIP activity, reconnaissance and known hostile sources.
Rapid, governed response
When behaviour reaches defined high-confidence thresholds, approved security policies can automatically restrict the hostile source and record what happened.
ITC threat intelligence
If the same hostile source begins probing several protected I.T Communications networks, the platform can correlate those security indicators centrally and increase threat confidence. Sufficiently high-confidence activity can contribute to an ITC-wide intelligence view.
Every protected ITC connection contributes to a broader picture of malicious internet activity.Private customer network data is not shared directly between customers.External threat intelligence
Active Network Protection automatically checks external source addresses against current intelligence from Spamhaus DROP and the DShield Recommended Block List. This adds established global reputation data to the activity seen across the protected I.T Communications estate.
Known hostile Spamhaus ranges can be proactively blocked under ITC security policy. DShield intelligence contributes to threat scoring and the governed response, helping the platform recognise dangerous sources sooner.
High-confidence hostile IPv4 and IPv6 ranges can be blocked at the managed router before traffic reaches services behind it.
Recommended hostile ranges strengthen risk scoring and can contribute to automatic protection when defined policy thresholds are reached.
Customer portal visibility
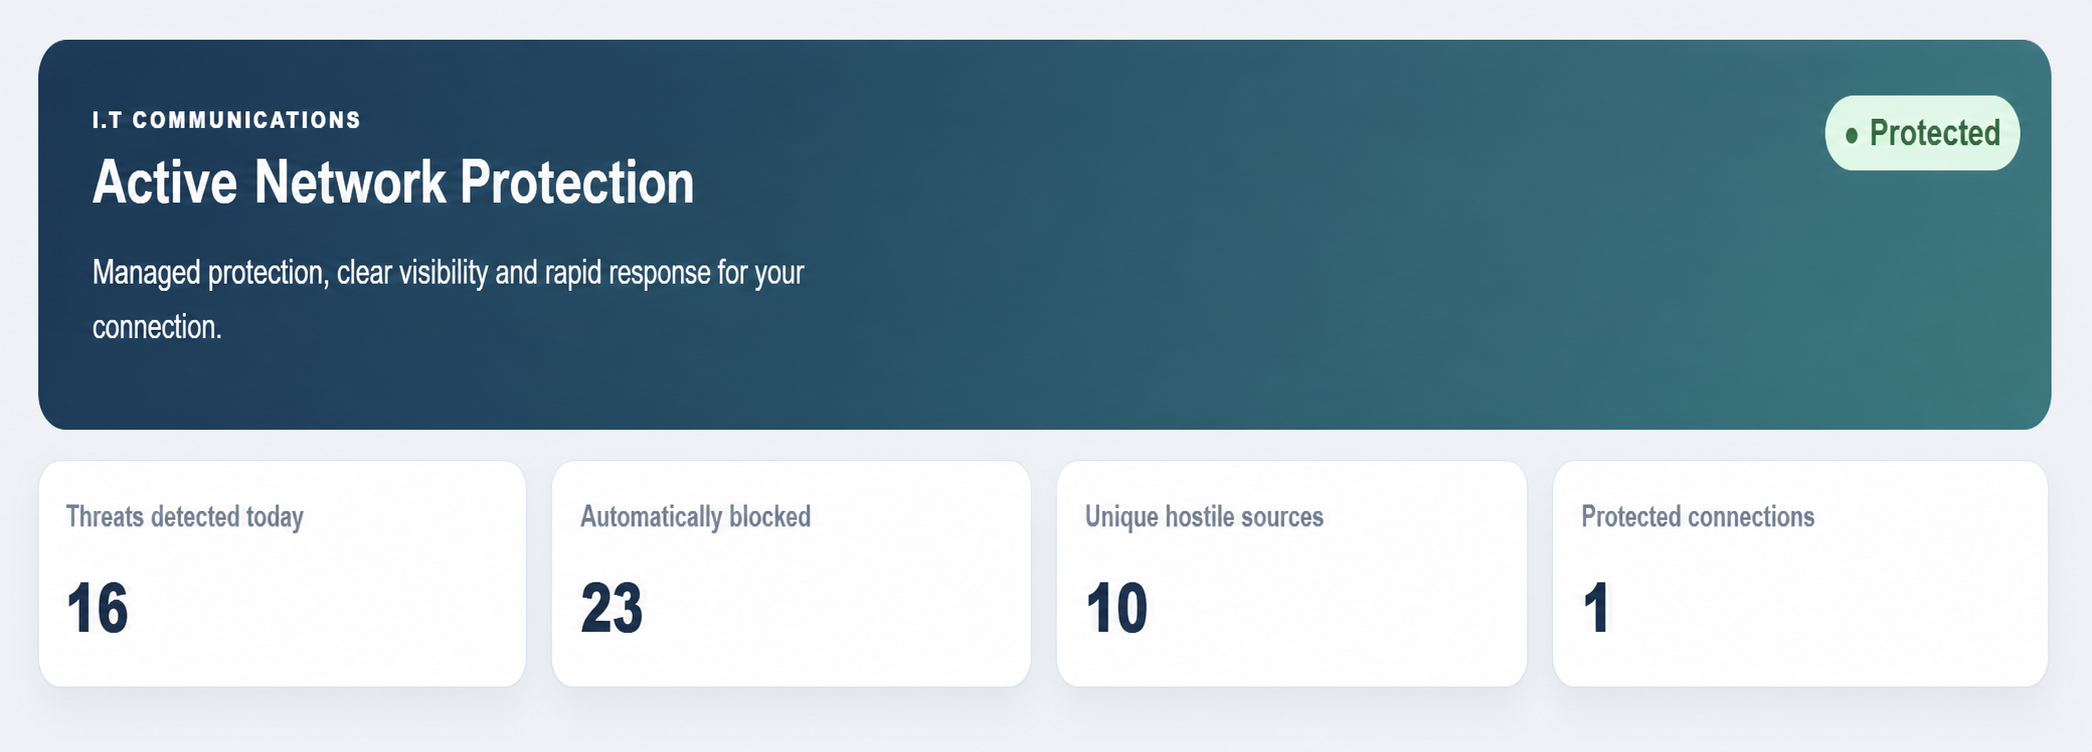
Review protection status, current threat level, detected and blocked activity, recent events, attack history and AI-generated incident explanations through the I.T Communications portal.
Your connection received a large number of attempts from one external source across multiple network services. The behaviour was consistent with automated network reconnaissance. Active Network Protection temporarily blocked the source in accordance with your security policy.
Advanced network monitoring, AI-powered analysis, automated threat response, security event history and portal visibility form part of eligible managed leased-line services.
Get a Leased Line QuoteAdd Active Network Protection as an optional monthly service to a supported I.T Communications managed broadband connection.
Ask About Active Network ProtectionMore than connectivity
Network activity is continuously analysed for suspicious behaviour.
High-confidence threats can be temporarily restricted without waiting for manual intervention.
AI adds context, correlates activity and explains incidents clearly.
Spamhaus and DShield intelligence helps identify known hostile source addresses.
Security indicators can be correlated across the protected ITC estate.
See threats, actions and network activity through your ITC portal.
No separate security appliance or additional dashboard to maintain.
Significant deviations from normal network behaviour can be identified.
A stronger connection
| Capability | Typical internet connection | ITC Active Network Protection |
|---|---|---|
| Internet connectivity | ✓ | ✓ |
| Continuous threat monitoring | — | ✓ |
| Automated threat response | — | ✓ |
| AI-powered analysis | — | ✓ |
| Customer security dashboard | — | ✓ |
| Cross-network threat intelligence | — | ✓ |
| Managed security visibility | — | ✓ |
Controlled automation
AI assists with understanding and classifying suspicious activity, but enforcement remains governed by predefined I.T Communications security policies. AI does not have unrestricted control of customer routers.
Where it adds value
Protect exposed services and understand suspicious internet activity.
Monitor supported managed connections across sites from one portal.
Identify suspicious SIP and scanning activity around business voice services.
Add another protection layer around critical leased-line connectivity.
Active Network Protection does not replace endpoint security, antivirus, EDR, email security, identity protection or a complete cyber-security strategy. It can identify and respond to certain hostile traffic and connection-flood patterns at the managed router; it cannot prevent every threat or overcome an access circuit already saturated upstream.
Managed connectivity, intelligently protected
Choose I.T Communications for continuous monitoring, automated threat response, AI-powered analysis and customer portal visibility in one managed service.
Active Network Protection included with eligible managed I.T Communications leased lines.